Millions of PHP Hosts Remain Exposed to Two PHP2Shell Vulnerabilities
Loading…
20 years of cybersecurity expertise, delivered through integrated and intelligent solutions for asset protection, threat detection and response, industrial security, and operational continuity.
Card 5 of 5
Card 1 of 4: Padvish
Protection of sensitive financial data, network access control, and detection and response across endpoints and servers, with centralized security management.
Protection for office and industrial environments, control of file transfers into isolated networks, and defense against cyber threats to reduce operational disruption.
Centralized security management across large-scale infrastructure, protection of endpoints and servers, and unified event analysis for effective threat detection and response.
Protection of sensitive information and organizational documents, access and file-transfer control, and defense of digital infrastructure to reduce data leakage and service disruption.
Security management across multiple organizations, protection of technical information and office/industrial systems, and controlled file exchange to reduce intrusion and production disruption.
Protection of sensitive data and service-support systems, access control, and cyber-threat defense to reduce information leakage and disruption of critical services.
Card 1 of 6: Banking, FinTech & Financial Services
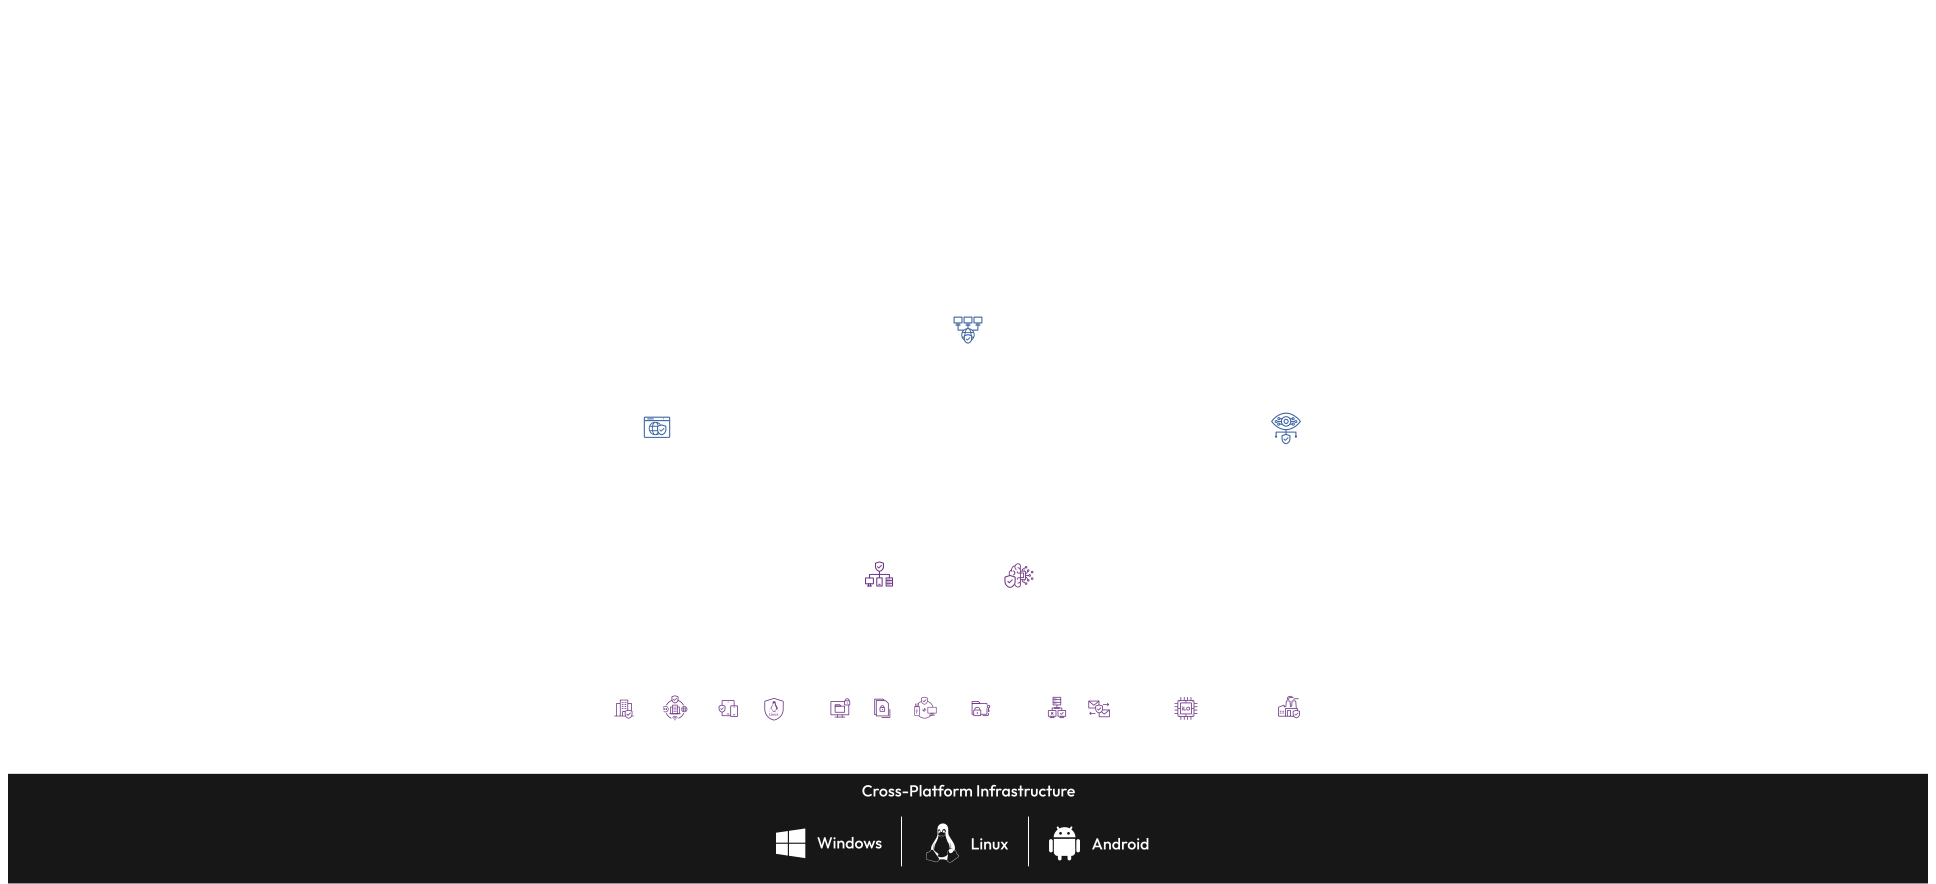
A four-layer diagram of Amnpardaz cyber defense. From outside to inside: Managed Products & Services, Agentic AI Defense Suite, Cloud Protection, and Padvish On-Premise Protection. The shared infrastructure at the bottom includes Windows, Linux, and Android. Use the layer controls to read each layer’s details.
Architecture overview; no layer is selected.
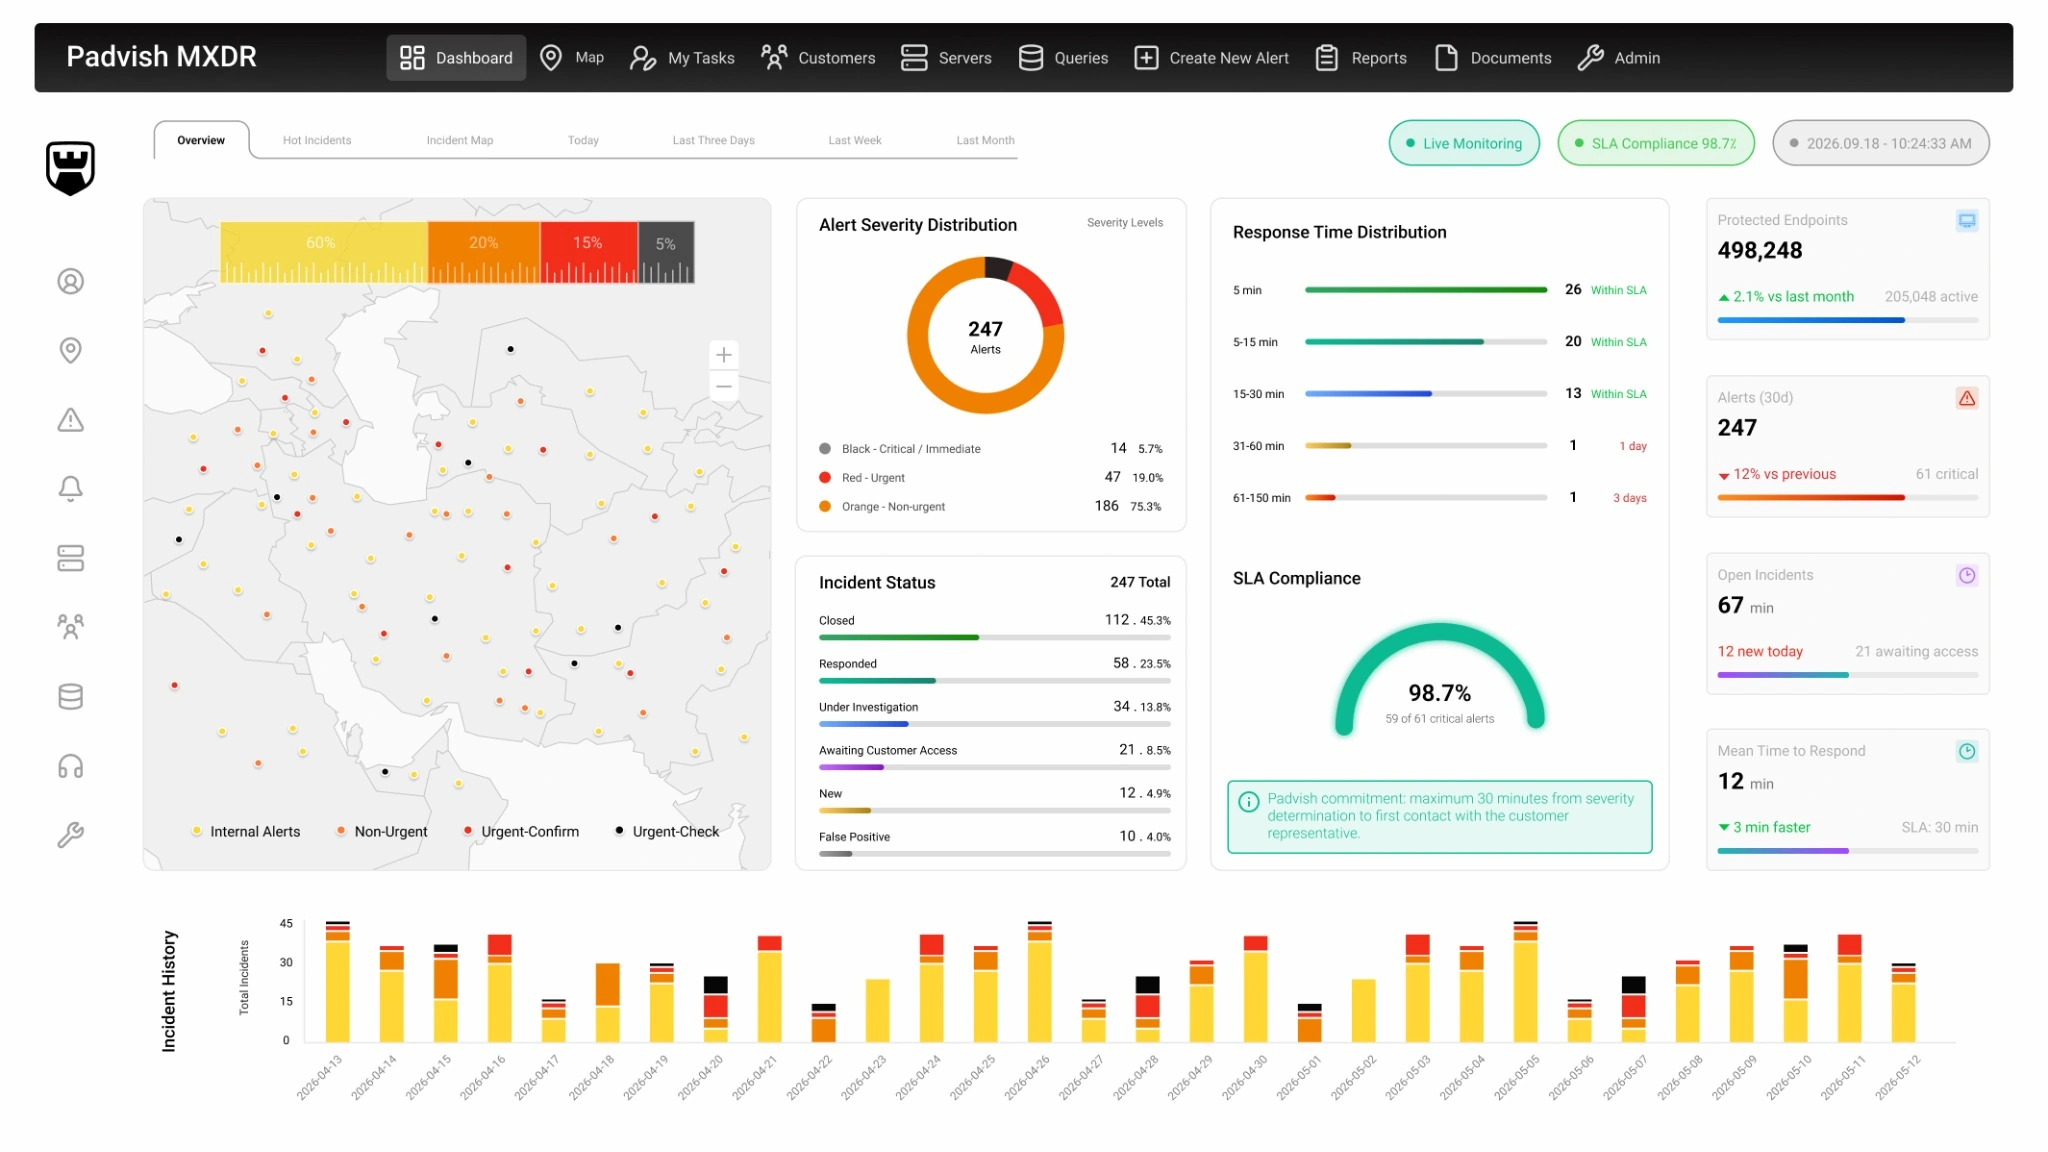
Padvish MXDR services provide specialized around-the-clock monitoring without the need for additional in-house personnel. Backed by a Service Level Agreement (SLA), the service takes responsibility for responding to cyberattacks and cyber threats.
Card 1 of 2
Proactive detection and neutralization of unknown malware within the organization, without data leakage.
Cyber Analyst™ simulates suspicious code behavior in isolated environments, extracts the logic of advanced attacks, and feeds the results directly into defensive layers without delay.
Isolated Sandboxing and Multi-Layer Simulation (Dynamic Sandbox):
Execute files safely in a quarantined environment and track registry changes, API calls, memory, and network communications.
Disassembly and Reverse Engineering with Defensive Intelligence:
Automatically identify antivirus evasion techniques (Evasion) and polymorphic malware without time-consuming manual analysis.
Complete Protection of Trade Secrets (Zero Data Leakage):
No need to upload organizational files to external platforms, ensuring complete confidentiality of source code and sensitive documents.
Coordinated Response and Real-Time EDR/XDR Updates:
Instantly convert malware analysis into indicators of compromise (IoCs) and automatically apply blocking policies across all organizational clients.
Turn hours of exhausting triage into seconds of decisive action, without increasing costs or staffing.
CyberGPT™ reads vast volumes of fragmented alerts in real time, reconstructs the intrusion chain, and increases your security team’s decision-making power tenfold through a fully local, isolated deployment.
Reduce Security Alert Fatigue by 95% (Automated Triage):
Intelligently correlate events and immediately distinguish routine network noise from genuine, high-risk threats.
Natural-Language Analysis and Queries (Natural Language to Telemetry):
Managers and analysts can retrieve the status of any asset with a simple text question, without mastering complex query languages.
Real-Time Dissection of Obfuscated Scripts:
Automatically analyze malicious PowerShell code, macros, and fileless process behavior (Fileless) before they spread within the organization.
Guaranteed 100% Data Sovereignty (Air-Gapped & On-Premise):
Local AI deployed in your data center, without a single byte of data, logs, or identity information leaving the organization’s boundaries.
Mitigation of DDoS attacks at Layers 3, 4, and 7 using dedicated scrubbing centers and a global BGP Anycast network for intelligent traffic distribution and prevention of network-layer attacks.
Deceive attackers, observe their behavior and collect tools and attack techniques through a cloud-based honeynet and honey traps.
Inspect the network the same way attackers see it and discover assets and vulnerabilities before they do with BlackBox scanning.
Not just IOC feeds, but early warnings about attacker intent through a threat intelligence platform (TIP).
Provide 24/7 proactive monitoring, incident response and increased cost and complexity for attackers through early detection and neutralization.
Automatically protect web services, networks and organizational email against unknown vulnerabilities and targeted attacks.
Deploy in pilot phases before rolling out across the organization.
Configure solutions carefully to avoid blocking critical organizational processes.
Provide step-by-step technical support when transitioning from previous security solutions to the new solution.
Monitor the update status and operational health of management servers in coordination with the organization’s security and network administrators.
When infections, unknown workstation behavior, or access disruptions occur, your ticket does not get stuck in an unclear process.
Have the technical analysis team examine suspicious files and behavior and provide tailored remediation instructions.
Receive support tailored to the contract type and the sensitivity of your infrastructure, from enterprise licenses to individually agreed service levels.
Use offline update and management methods designed for networks without internet access (Air-Gapped).
Support distributed architectures and apply policies consistently across organizational branches.
Amnpardaz’s security architecture team is ready to demonstrate the capabilities of its integrated cyber defense platform in a technical demo session.