Loading…
Continuous monitoring and intelligent response for all endpoints, identifying, analyzing, and stopping threats before they spread.
Advanced Endpoint Detection and Response (EDR) certification from the AV-TEST institute, Germany
The Padvish EDR AI system is an advanced solution for organizations that require continuous oversight of suspicious activities and wish to establish client security at a level beyond traditional tools.
The Padvish EDR AI system detects infiltration the moment it forms by utilizing artificial intelligence and machine learning. By analyzing application behavior, this system prevents data deletion and identifies signs of infection across the entire organizational network.
The Padvish intelligent detection and response system enables threat hunting, memory monitoring, and the use of IPS. With automated response and precise reporting, it provides the necessary foundation for rapidly tracing the root cause of attacks.
Be armed against infiltration and hidden organizational threats with Padvish.

Identifying Indicators of Compromise (IOCs) to detect malicious activities

Monitoring system memory for potential cyberattacks, such as malware decryption

Analyzing system process behavior to detect suspicious patterns of cyberattacks

Using algorithms to detect security threats and identify suspicious code patterns

Detecting and protecting against network attacks like Log4j and ZeroLogon

Executing files in a virtual environment to detect and analyze security threats
Identifying Indicators of Compromise (IOCs) to detect malicious activities
Monitoring system memory for potential cyberattacks, such as malware decryption
Analyzing system process behavior to detect suspicious patterns of cyberattacks
Using algorithms to detect security threats and identify suspicious code patterns
Detecting and protecting against network attacks like Log4j and ZeroLogon
Executing files in a virtual environment to detect and analyze security threats
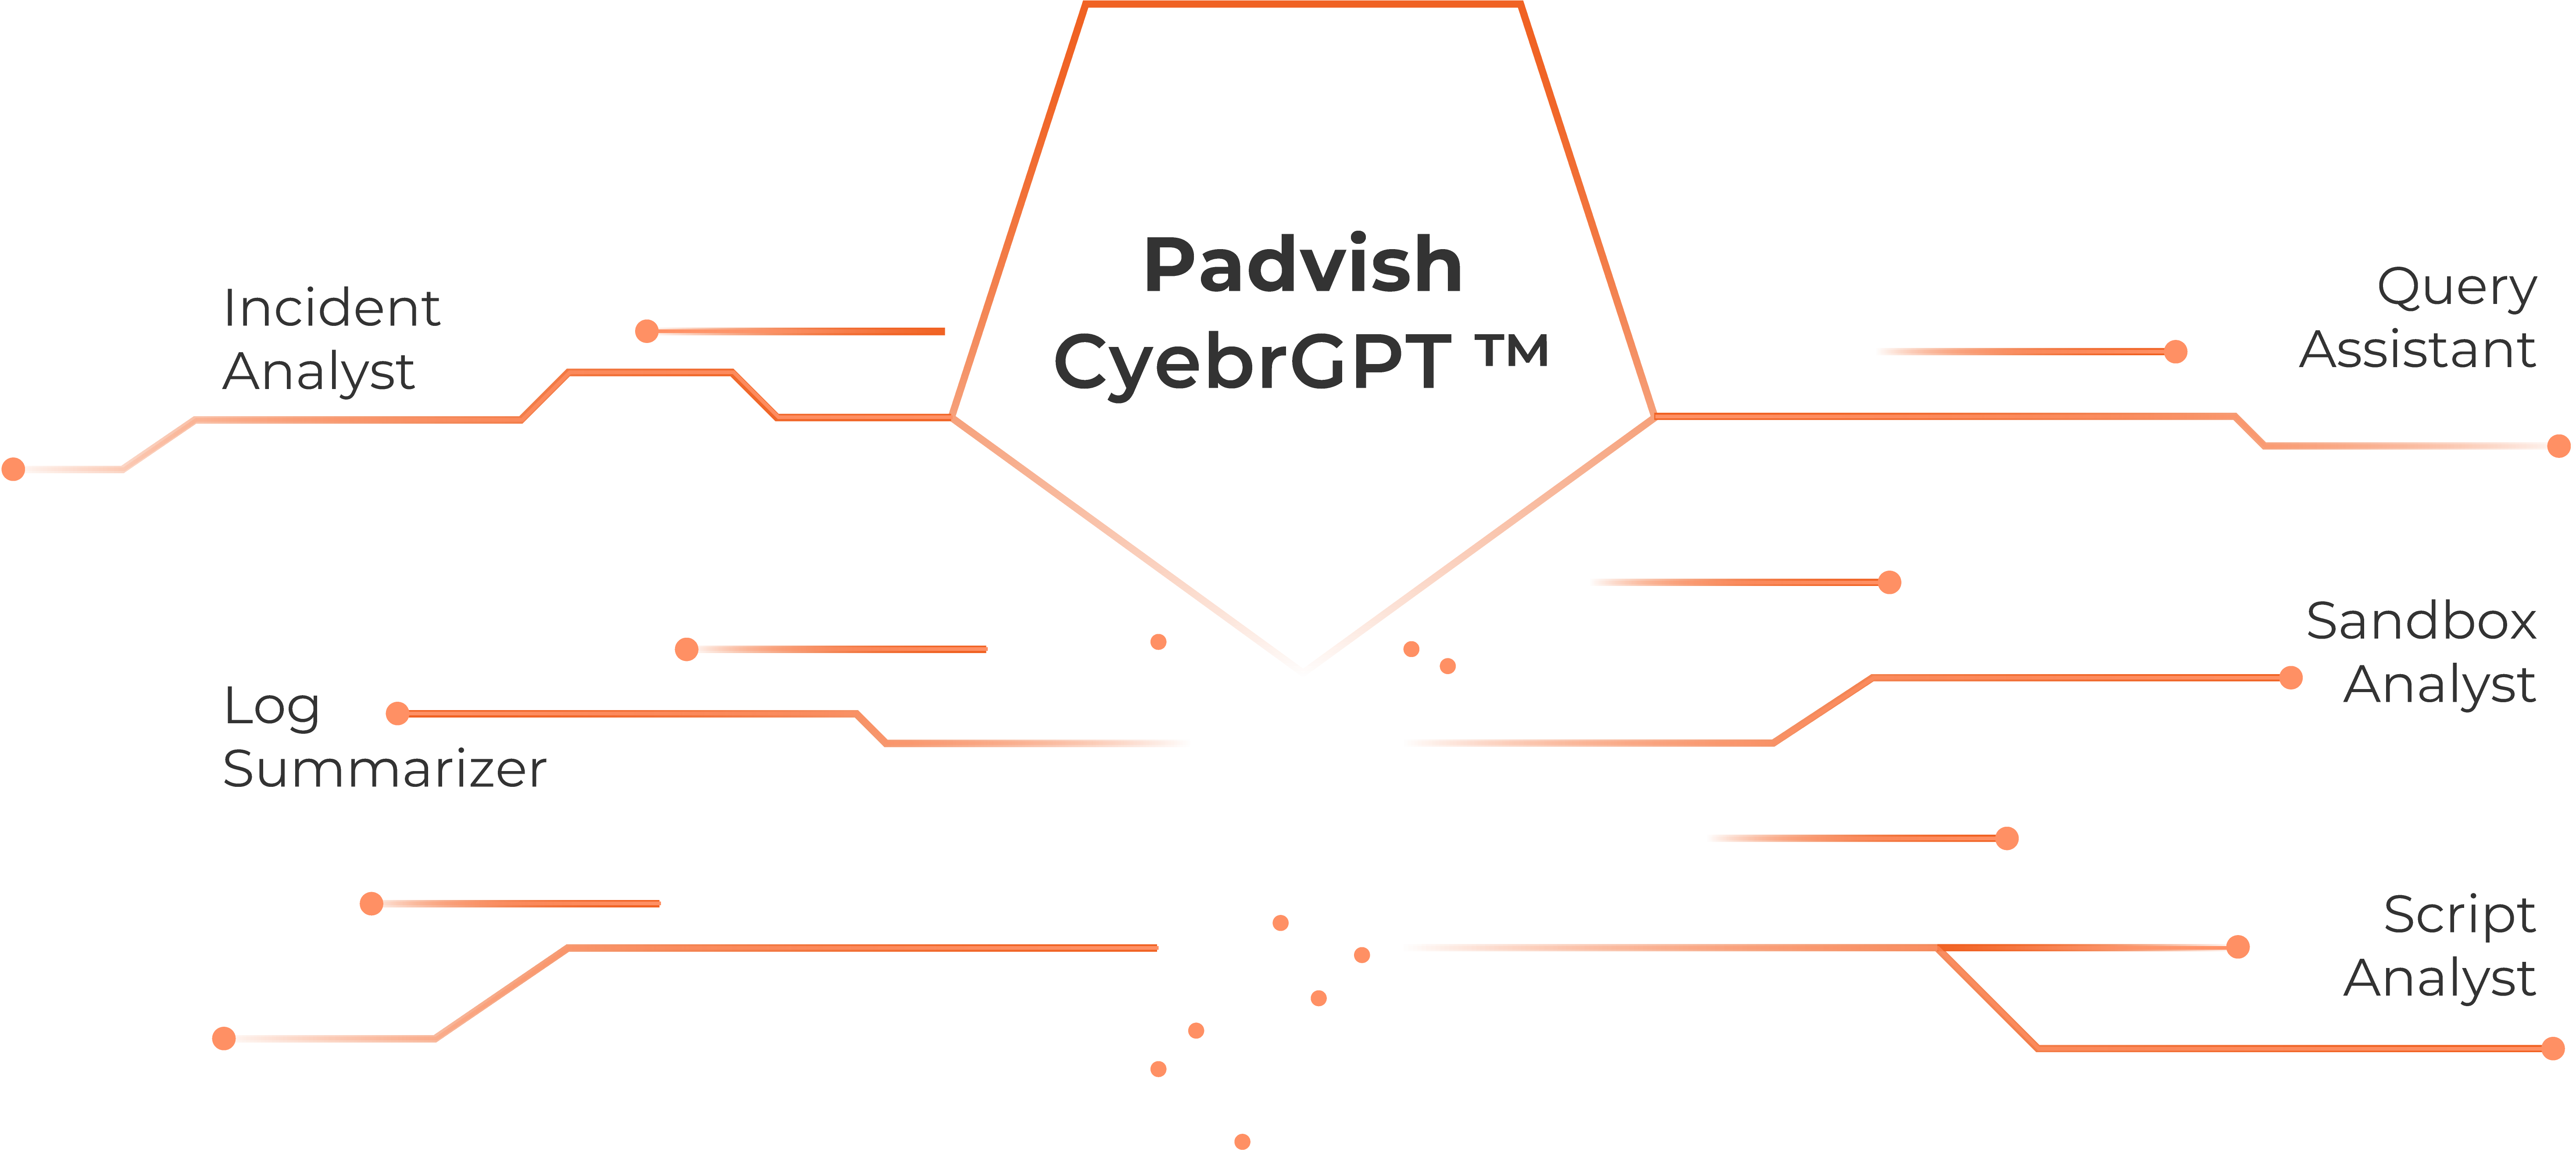
While security teams constantly strive to detect and prevent attacks in their early stages, threat prevention may not always achieve 100% success; this is because monitoring and analyzing all events without access to the necessary tools is a major challenge.
The Padvish EDR system, as a unified endpoint security solution, continuously combines capabilities for continuous monitoring, deep analysis, and real-time response. This system is highly recommended for organizations seeking a comprehensive and powerful solution to combat complex and persistent threats.


 Anti-MalwareMemory ScannerBehavioral ProtectionMachine LearningIntrusion Prevention SystemFile LibrarySandboxDetection EnginesSuspicious File AnalyzerPadvish CyberGPT™

 Anti-MalwareMemory ScannerBehavioral ProtectionMachine LearningIntrusion Prevention SystemFile LibrarySandboxDetection EnginesSuspicious File AnalyzerPadvish CyberGPT™Anti-MalwareMemory ScannerBehavioral ProtectionMachine LearningIntrusion Prevention SystemFile LibrarySandboxDetection EnginesSuspicious File AnalyzerPadvish CyberGPT™Anti-MalwareMemory ScannerBehavioral ProtectionMachine LearningIntrusion Prevention SystemFile LibrarySandboxDetection EnginesSuspicious File AnalyzerPadvish CyberGPT™

Unified management, configuration, monitoring, and updates

Fast deployment and reduced administrative overhead
Have a question?We are here to answer