Loading…
Managed security solution based on Padvish EDR AI, with 24×7 monitoring and rapid response
Advanced Endpoint Detection and Response (EDR) certification from the AV-TEST institute, Germany
Padvish Managed Detection and Response (MDR) is a comprehensive solution built on Padvish EDR AI, designed to provide organizations with centralized network visibility while addressing operational gaps caused by limited access to specialized security personnel.
Padvish MDR is a centralized security solution built on a combination of specialized expertise and advanced technology. Based on operational experience from previous attacks, the service aggregates, classifies, and analyzes data collected across the organizational network to identify intrusions and prevent the continuation of malicious activity.
Padvish MDR services are designed to support the protection of organizational networks against advanced threats. By leveraging technologies such as sandboxing, EDR, and malware analysis laboratories, the solution enables structured response to targeted attacks and contributes to improving the overall cybersecurity posture of the organization.
Padvish security specialists act as an active and continuous operational layer for monitoring organizational network security.

Continuous monitoring of networks and endpoints to identify threats at any time.

Network, data, and behavioral analysis designed to identify and mitigate potential threats.

Identification of attacks, assessment of vulnerabilities, and execution of rapid response actions against threats.

Service equipped with dedicated monitoring and management capabilities.

Periodic reporting on network status and security conditions.

Service levels designed to align with organizational requirements.

Advanced multi-layer sensors designed for rapid and accurate threat detection.

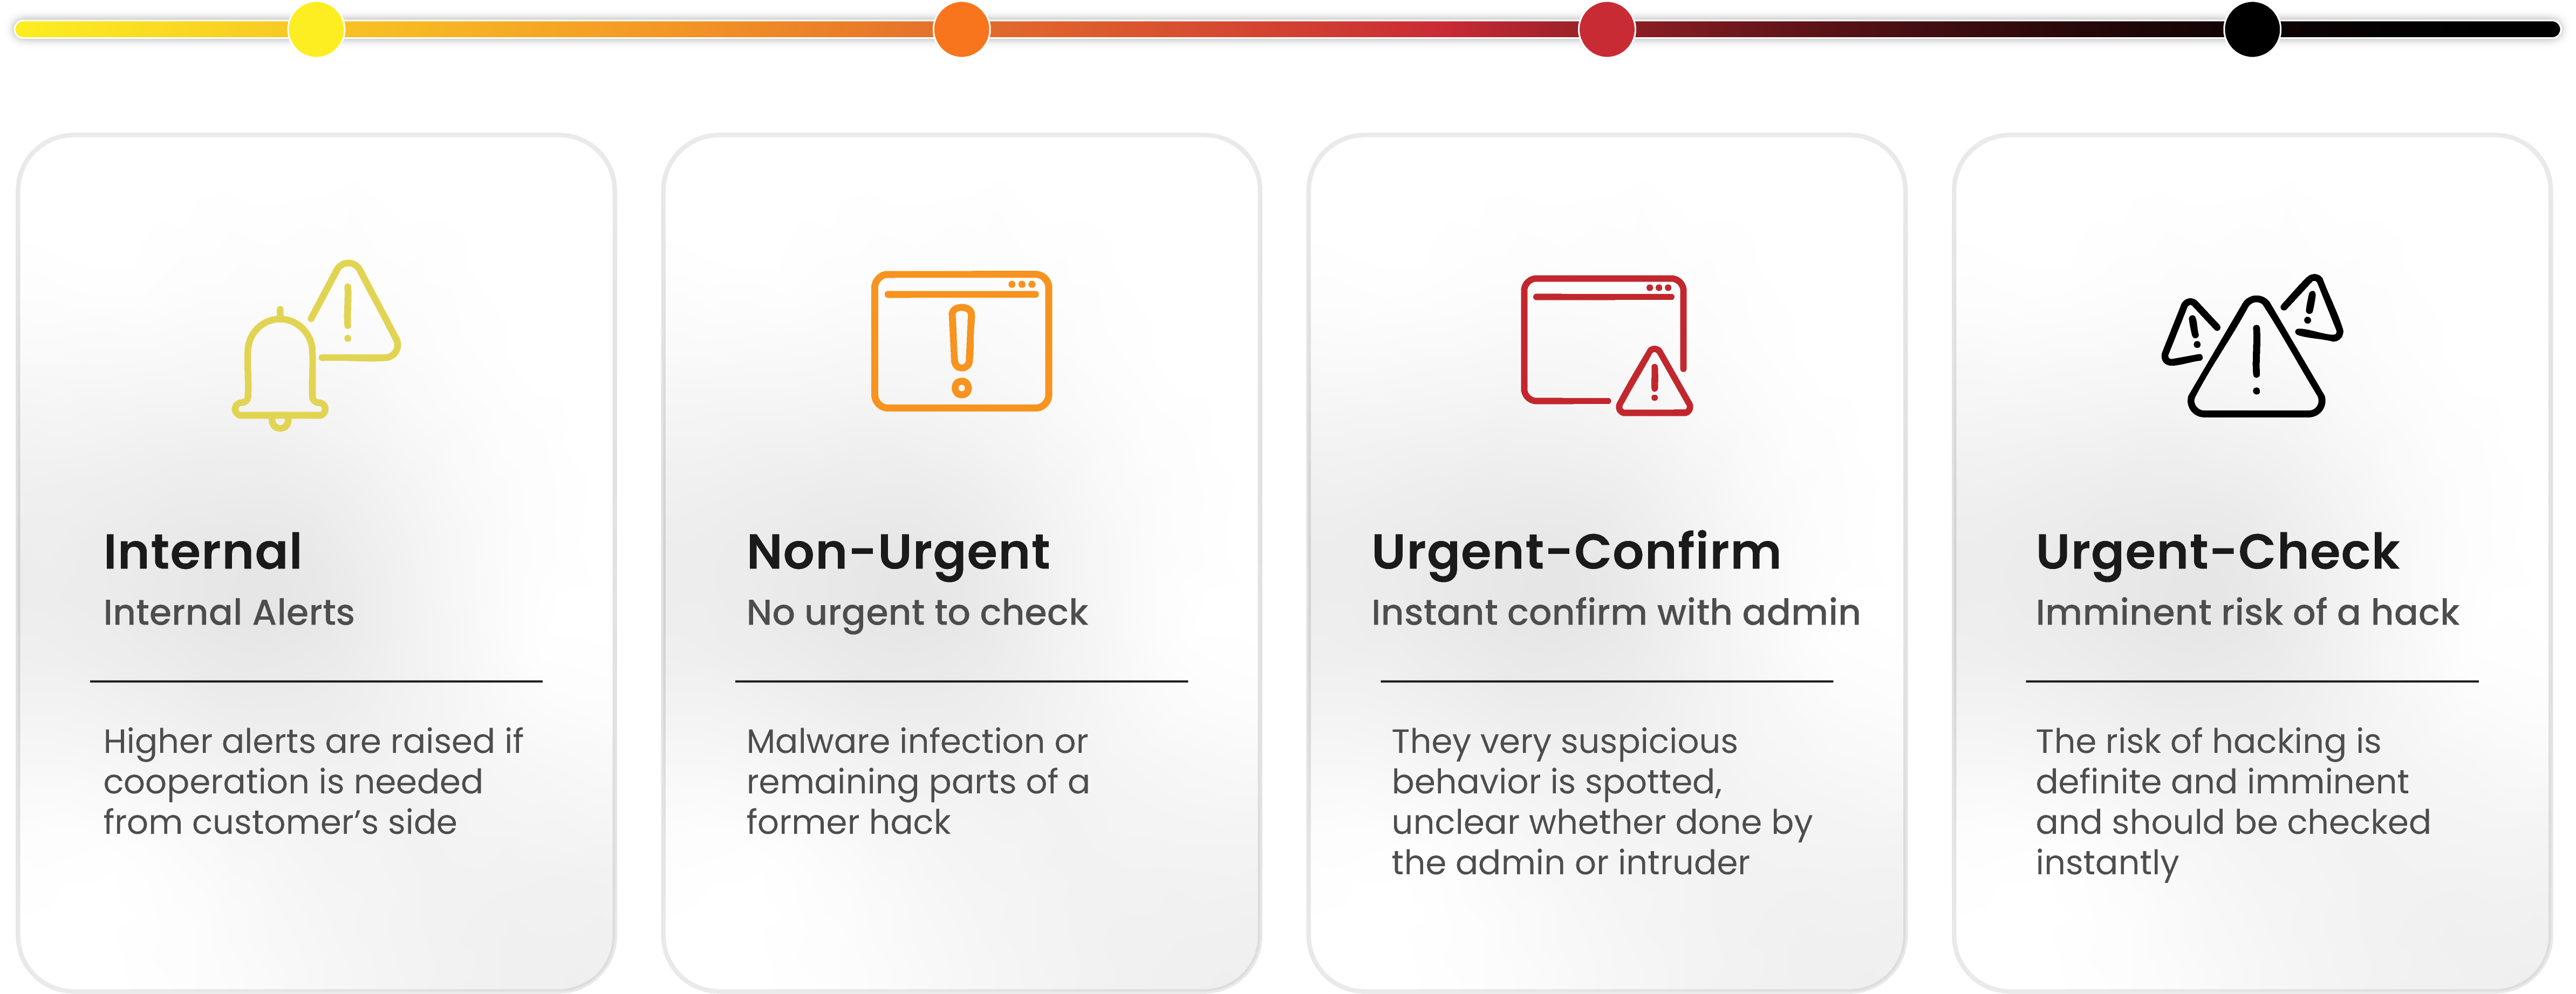
Classification and prioritization of alerts, followed by customer notification after confirmation of an active threat.

Reporting of vulnerabilities and areas for security improvement within the network.
Continuous monitoring of networks and endpoints to identify threats at any time.
Network, data, and behavioral analysis designed to identify and mitigate potential threats.
Identification of attacks, assessment of vulnerabilities, and execution of rapid response actions against threats.
Service equipped with dedicated monitoring and management capabilities.
Periodic reporting on network status and security conditions.
Service levels designed to align with organizational requirements.
Advanced multi-layer sensors designed for rapid and accurate threat detection.
Classification and prioritization of alerts, followed by customer notification after confirmation of an active threat.
Reporting of vulnerabilities and areas for security improvement within the network.
 Limited MonitoringTraining RequirementOperational Monitoring RequirementDeep Sensors
 Comprehensive Attack MonitoringOperational Experience in Threat ResponseSpecialized Security Experts24×7 MonitoringDeep Sensors
Organizations may operate the Padvish EDR platform internally through their own cybersecurity teams. However, the Padvish MDR service enables organizations to benefit from the operational expertise of Padvish specialists to improve security posture against a wide range of attacks with reduced operational overhead.
24/7 MonitoringAn experienced expert team with experience in investigating recent cyberattacksThe depth of advanced sensorsSecurity alert notificationAlert notification via text message/callAlert written noticeActive threat huntingGuaranteed service levelAlert retention for up to one yearPeriodic network status reportsForensics operations up to a specified time limitNetwork security posture assessmentReporting the weaknesses and improvable aspects of the networkRaw log retention for the period specified by the organization’s policyAccess to the Padvish EDR web interface
 24/7 MonitoringAn experienced expert team with experience in investigating recent cyberattacksThe depth of advanced sensorsSecurity alert notificationAlert notification via text message/callAlert written noticeActive threat huntingGuaranteed service levelAlert retention for up to one yearPeriodic network status reportsForensics operations up to a specified time limitNetwork security posture assessmentReporting the weaknesses and improvable aspects of the networkRaw log retention for the period specified by the organization’s policyAccess to the Padvish EDR web interface24/7 MonitoringAn experienced expert team with experience in investigating recent cyberattacksThe depth of advanced sensorsSecurity alert notificationAlert notification via text message/callAlert written noticeActive threat huntingGuaranteed service levelAlert retention for up to one yearPeriodic network status reportsForensics operations up to a specified time limitNetwork security posture assessmentReporting the weaknesses and improvable aspects of the networkRaw log retention for the period specified by the organization’s policyAccess to the Padvish EDR web interface

24×7 monitoring designed to identify threats as they emerge.

Experienced team specialized in cyberattack analysis and response.

Use of advanced sensors for more precise threat detection.

Immediate alerts delivered through SMS or direct contact for security-related events.

A fully managed service designed to cover endpoint threat detection and response operations.

Improved visibility across the network and strengthened overall threat defense capabilities.

Comprehensive network assessment for identifying vulnerabilities.

Isolated environment for safely testing executable files without affecting the network.

Unified management, configuration, monitoring, and updates

Fast deployment and reduced administrative overhead
Have a question?We are here to answer